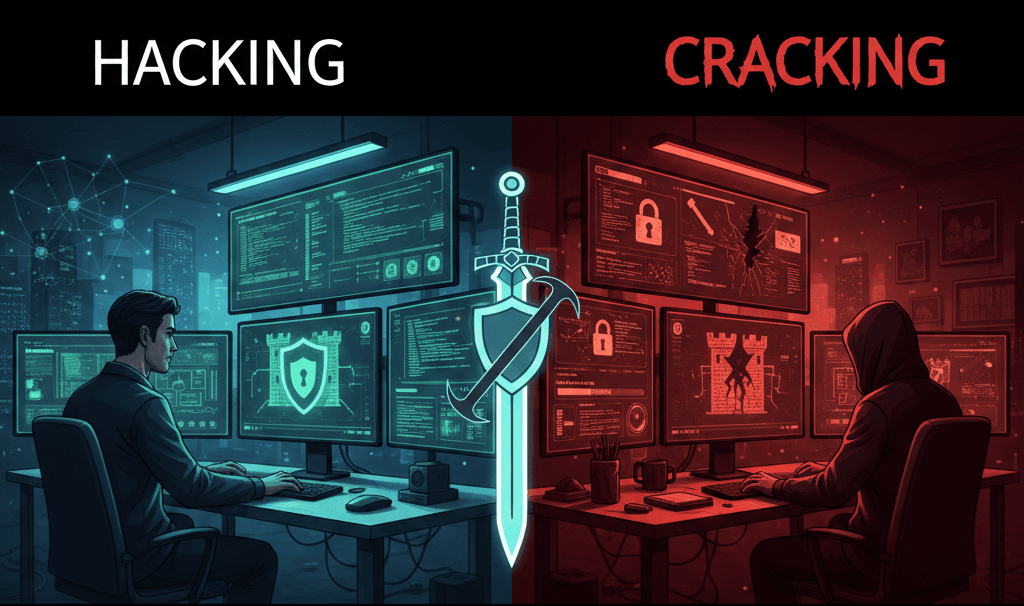
What is Hacking and Cracking?
In the world of cybersecurity, “hacking” and “cracking” are often used interchangeably by the general public, but they carry very…
Keeping You Protected
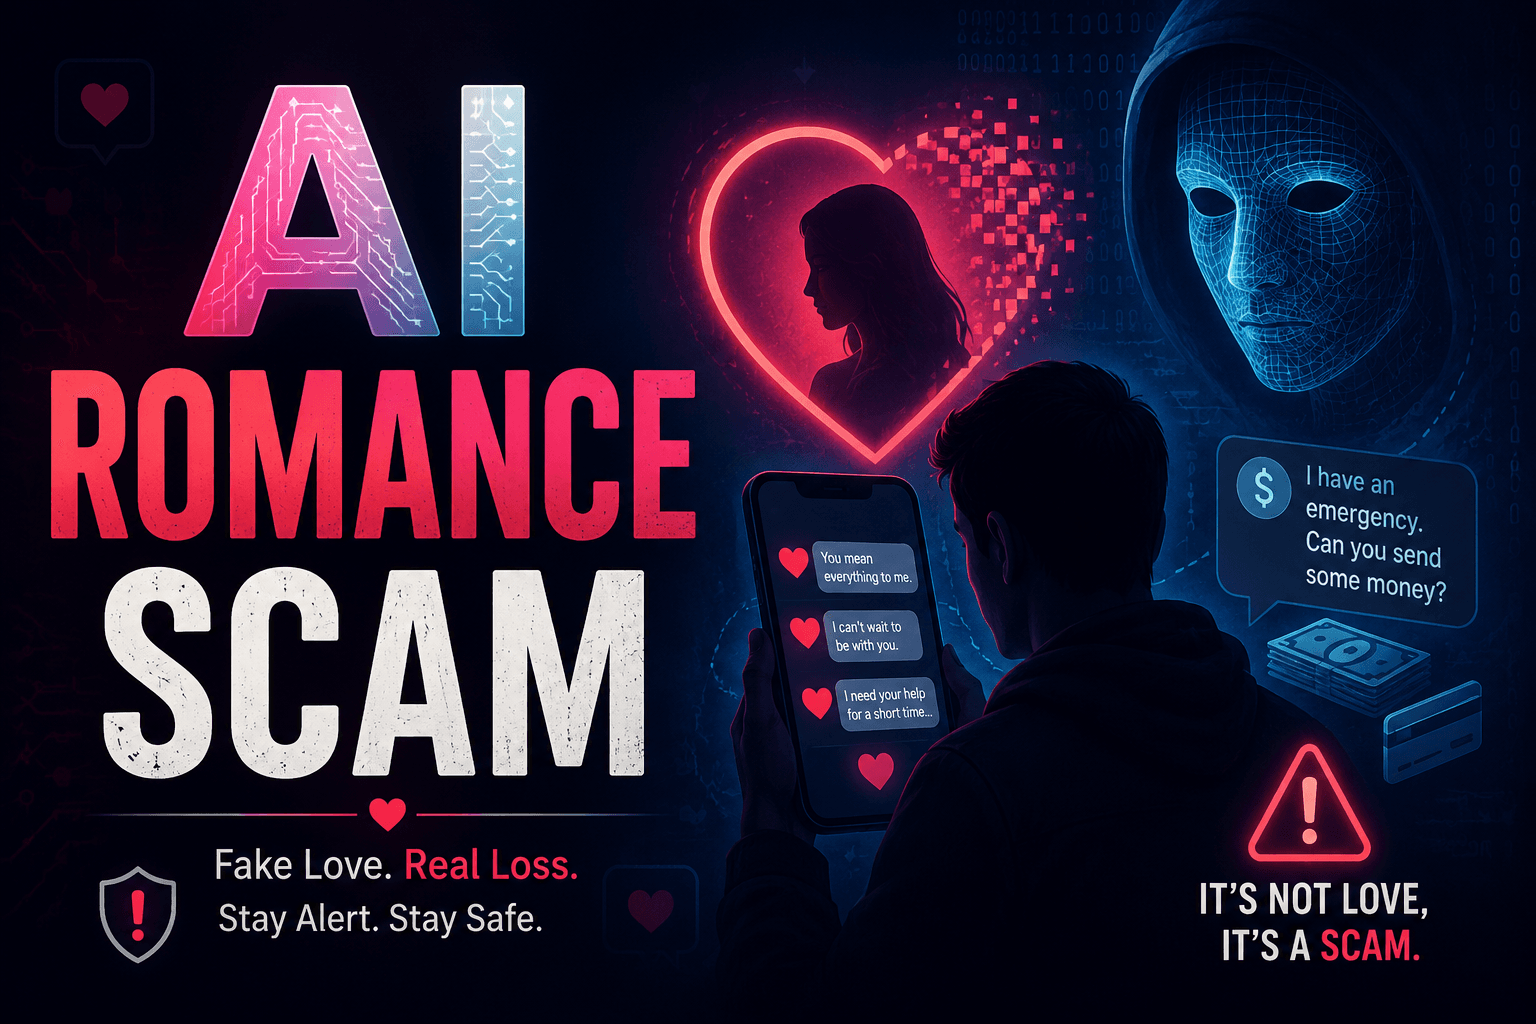
An AI Romance Scam is an advanced form of confidence fraud where cybercriminals use Artificial Intelligence to create synthetic personas,…
In the world of cybersecurity, “hacking” and “cracking” are often used interchangeably by the general public, but they carry very…
SQL Injection (SQLi) is a critical security vulnerability that occurs when an attacker “injects” malicious SQL code into a web…
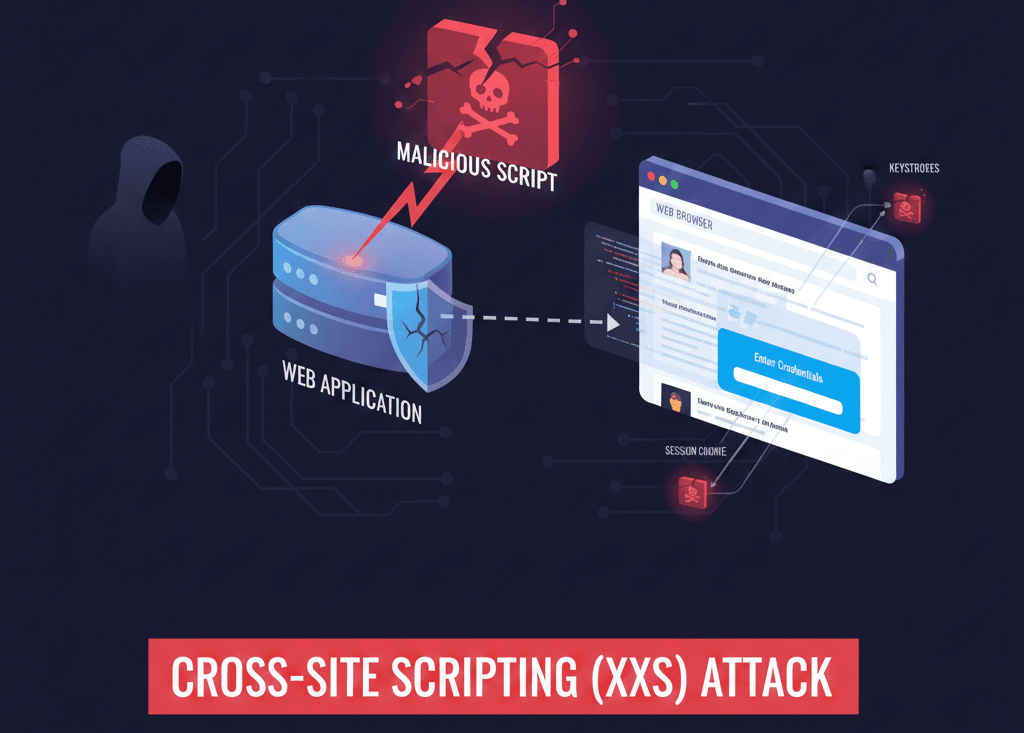
Cross-Site Scripting (XSS) is a type of security vulnerability typically found in web applications. It allows an attacker to inject…
A Scam Call Center is an organized, business-like operation where groups of fraudsters often called “agents” work in a professional…
A Brute Force Attack is a cryptographic hack that uses trial and error to guess login credentials, encryption keys, or…
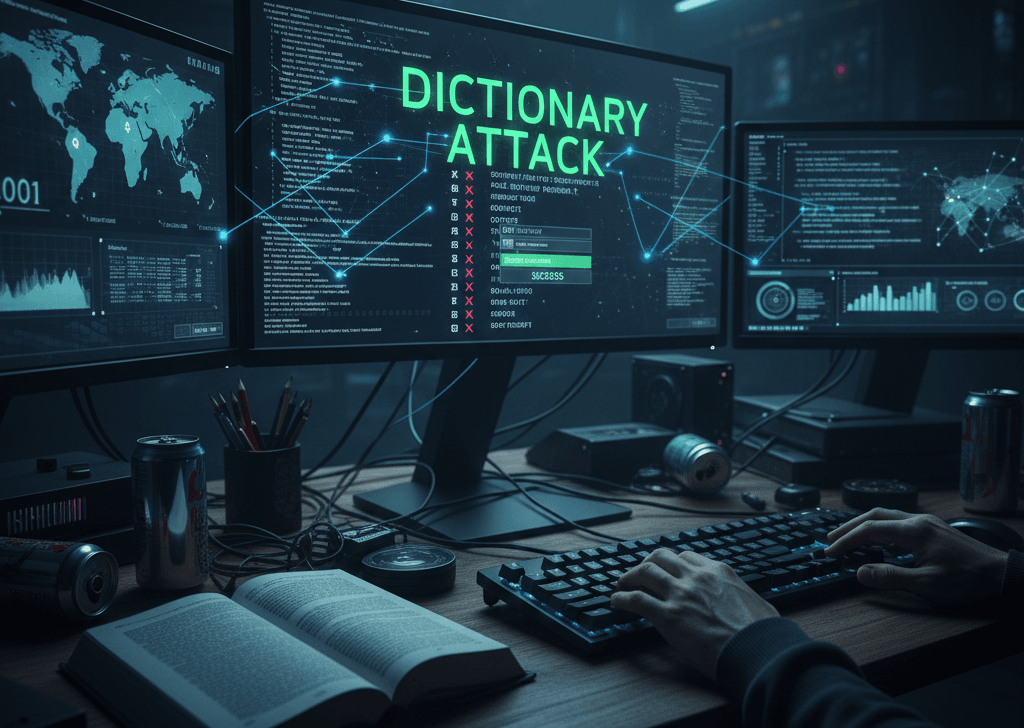
A dictionary attack is a method used by hackers to break into password-protected accounts by systematically entering every word in…
Fileless malware is a type of cyberattack that operates entirely in a computer’s memory (RAM) rather than being stored in…
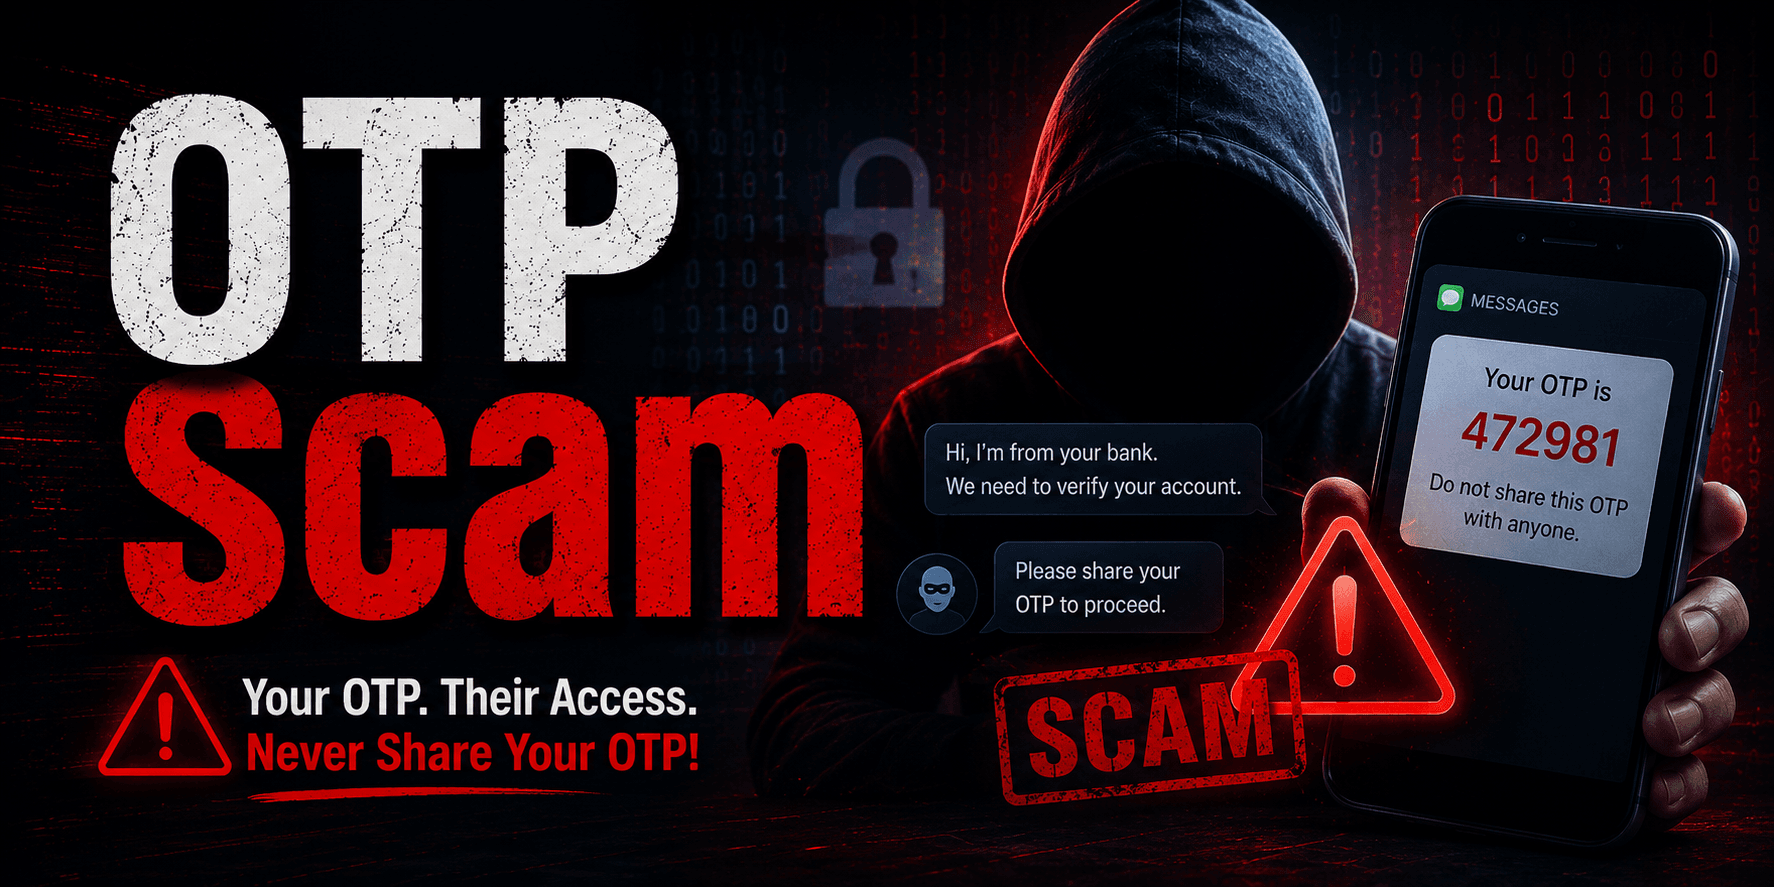
An OTP (One-Time Password or One-Time Pin) Scam is a type of fraud where a criminal tricks you into sharing…
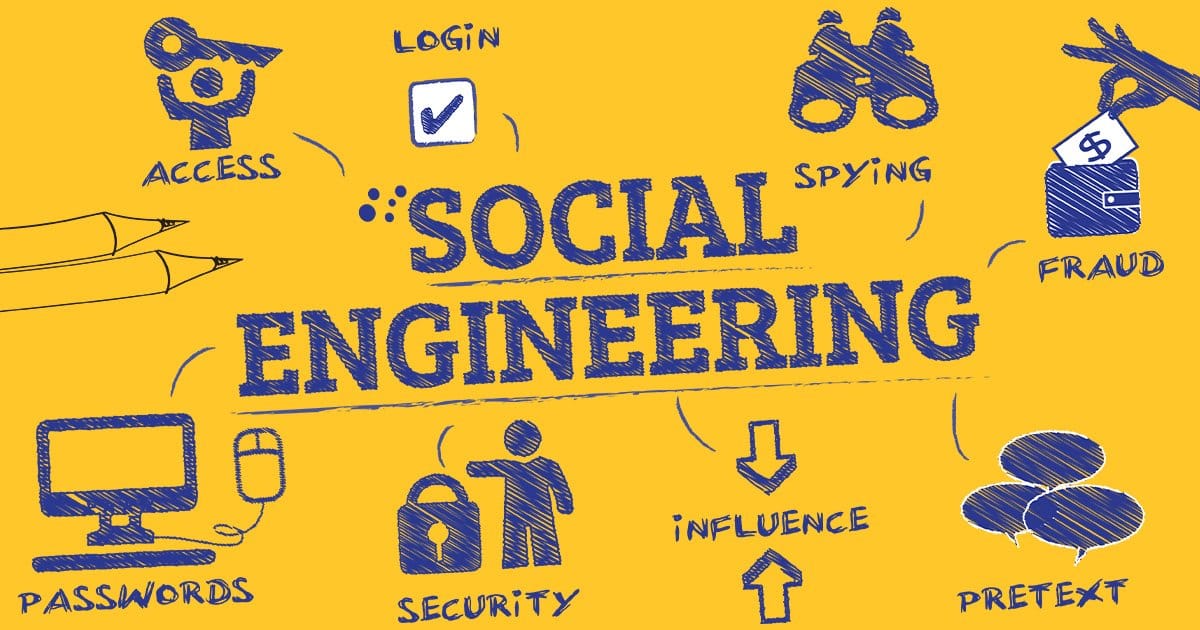
In cybersecurity, social engineering is the art of manipulating people into giving up confidential information or performing actions that compromise…